Showing items from Microsoft Intune

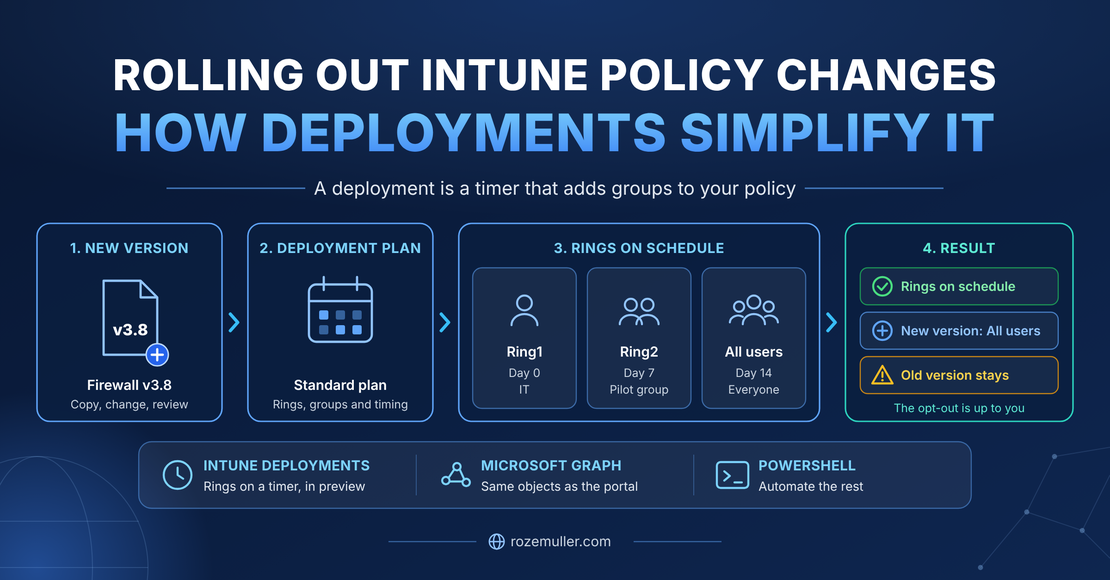
Rolling Out Intune Policy Changes, Part 1: Intune Deployments Plans, The Process and How Deployments Fit In

Rolling out a change to an Intune policy in a safe way is more a process question than a tooling question. In this series I explain how I look at that process, how Intune Deployments (now in public preview) take over a big part of it, how what you click in the portal looks in Graph, and how to automate the rest with PowerShell.

Continue Reading
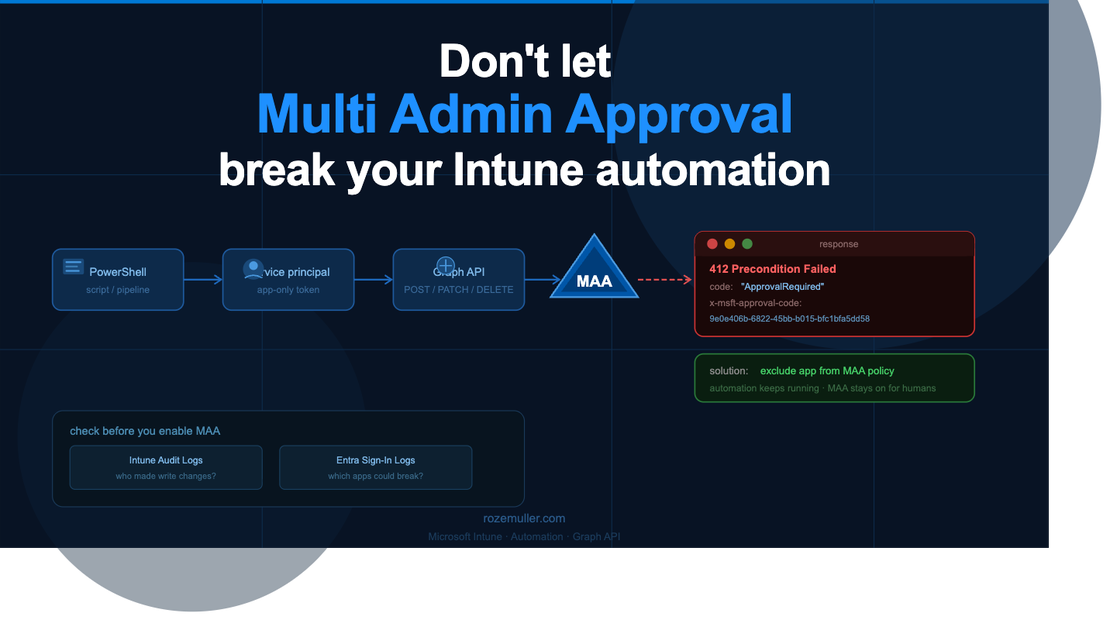
Don't Let Multi Admin Approval Break Your Intune Automation

Microsoft announced that Multi Admin Approval (MAA) now also applies to Graph API calls made by apps and service principals. Until now MAA only applied when an admin made changes in the Intune portal. But that changed. From now on, automated scripts and tools that use app-only tokens are intercepted too.

Continue Reading

Automated Device Group Management for Microsoft Intune Update Rings Using PowerShell

Testing settings and updates in Microsoft Intune is a good idea. Many Intune administrators use a test group and Deployment Rings for this. In the case of Windows Updates, administrators configure an update ring and assign a group to it. The group is filled with devices (I call it a device group). In this blog post, I will show you how to dynamically manage a device group in an automated way for your Intune update rings based on a user group. Let’s call it dynamic device group management.

Continue Reading

Monitor Security Baseline Insights Recommendations

Microsoft has updated their security baselines in Microsoft Intune which you can read in the What is new in Intune. A part of the updates is that Microsoft has added recommended settings based on your organisation. In this blog post, I show how to monitor these recommendations that are part of the security baseline and generate a response when a setting does not met Microsoft’s recommendation.

Continue Reading